wgcert
OPEN SOURCE / PUBLIC BETA

Renewed certificates, deployed to your Firebox.

wgcert is a small CLI that sends already-issued TLS certificates from Certbot, acme.sh, or your CA to cloud-managed WatchGuard Fireboxes through the official API.

Early validation: tested offline against mock API servers. Real Firebox testers wanted.

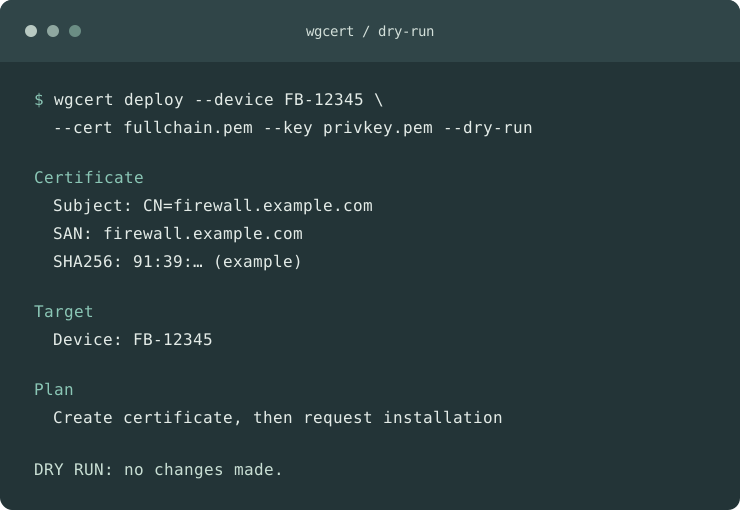
Illustrative terminal output showing wgcert dry-run certificate metadata and a mutation-free deployment plan01 / Inspect before you deploy

THE WORKFLOW

Keep issuance where it already works.

Certbot or acme.sh renews the certificate. wgcert validates the files, uses the WatchGuard API to create and install the certificate, and can check the TLS endpoint you specify.

01ACME clientRenews certificate
02wgcertValidates and deploys
03WatchGuard CloudCertificate API
04FireboxVerify intended service

BUILT FOR OPERATORS

A deploy step you can inspect.

A / 01

Dry-run before mutation

Parse the certificate, confirm the private key matches, inspect its SHA-256 fingerprint, and see the intended API steps before sending a create or install request.

wgcert deploy --device FB-12345 --cert fullchain.pem --key privkey.pem --dry-run
B / 02

Reuse matching certificates

A repeat run can reuse a remote certificate with the same fingerprint. Because the API inventory does not prove the device's active certificate, installation may still be requested again.

C / 03

Check the TLS endpoint

Compare the certificate served by a host with the local fingerprint. TLS verification checks the actual connection; API metadata alone cannot prove a service changed.

START HERE

A small first test.

Download a beta binary, set your regional WatchGuard Cloud API credentials, discover your device, then run a dry-run. Try mutations only on a disposable test Firebox.

Download v0.1.0 prerelease
wgcert devices

wgcert deploy \
  --device FB-12345 \
  --cert fullchain.pem \
  --key privkey.pem \
  --dry-run

wgcert check \
  --device FB-12345 \
  --verify-host firewall.example.com:443

CURRENT SCOPE

Know what has been verified.

Cloud-managed Fireboxes only. WatchGuard's certificate API does not support locally-managed devices.

Install is asynchronous. An accepted API command does not establish that your intended Firebox service is serving the new certificate.

Configuration deployment is opt-in. It may distribute all pending changes for that device. Review them first.

Real-device validation is still open. The project has unit tests and mocked API tests; a real renewal cycle remains the decisive test.

HELP VALIDATE THE NEXT STEP

Do you manage WatchGuard Fireboxes?

We are looking for operators who can test on cloud-managed Firebox or FireboxV and report which service uses the certificate, whether renewal references survive, and what the device actually serves.

Share a Firebox test